Signed Sidecar
A ticket authenticates a record identifier while the requested operation travels beside it. Determine whether every security-sensitive field is covered.
Objective
- Infer a MAC's effective scope by changing one field at a time.
- Explain why authorization context must be bound to authenticated data.
Before you begin
Open /challenge/hard/scope and preserve the complete signed link it provides. Read the linked record service integration reference. Its parameter, operation, and response tables provide the vocabulary needed for independent investigation.
Concepts
A valid MAC proves integrity only for the bytes included in its input. An unsigned action beside a signed object can be changed without invalidating the object's tag.
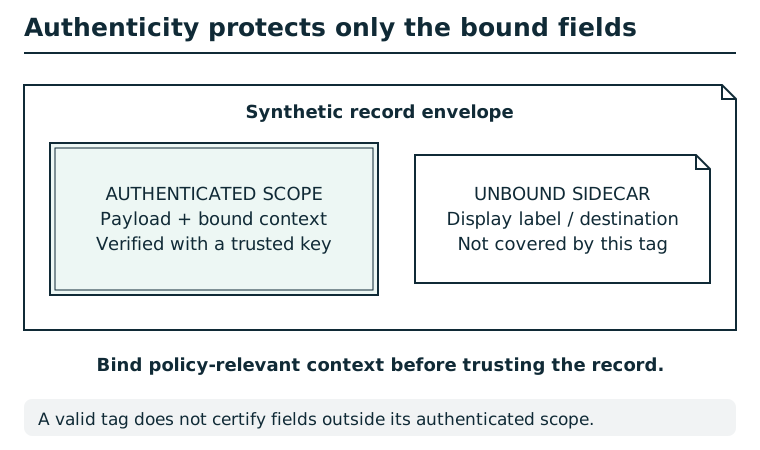
Protection applies to the exact bytes or canonical fields included in verification. A valid signature on a payload does not authenticate an adjacent label, destination, or policy field. Define and authenticate every security-sensitive field, verify the trusted signer, and enforce policy. An unkeyed digest alone does not establish publisher authenticity.
Suggested tools
- Browser or HTTP client: Edit one query field while preserving the record and signature exactly.
Tool practice
Rehearse the worked tool exercise before using challenge data.
Copy the complete original link before editing. Preserve the MAC text exactly and keep a table of changed field, signature accepted/rejected, and operation result. Read the integration reference alongside those observations; distinguish an unsupported operation from a rejected signature.
Investigation
Observe
Inventory the link's record, action, and signature fields. Follow it once to observe the ordinary operation. Read the reference's operation descriptions and record which outputs and errors the service documents.
Form a hypothesis
Which fields can change without causing signature rejection? Use the operation names in the reference to construct a meaningful comparison.
Test carefully
Change one field at a time and use signature acceptance or rejection to map the authenticated scope.
Progressive hints
Hint 1
Compare the supplied URL with the parameter and operation tables in the integration reference.
Hint 2
The page says the action travels beside the signed record.
Hint 3
Test the policy field that travels beside the signed object.
Troubleshooting and reset
Copy the original link again if the signature was altered or URL-decoded incorrectly. No server reset is required. If the challenge page has no reference link, the board needs the artifact update before this guide applies.